BUILT PRODUCTAI & Developer ToolsStudio-built
Building
AuthScan logo

AuthScan

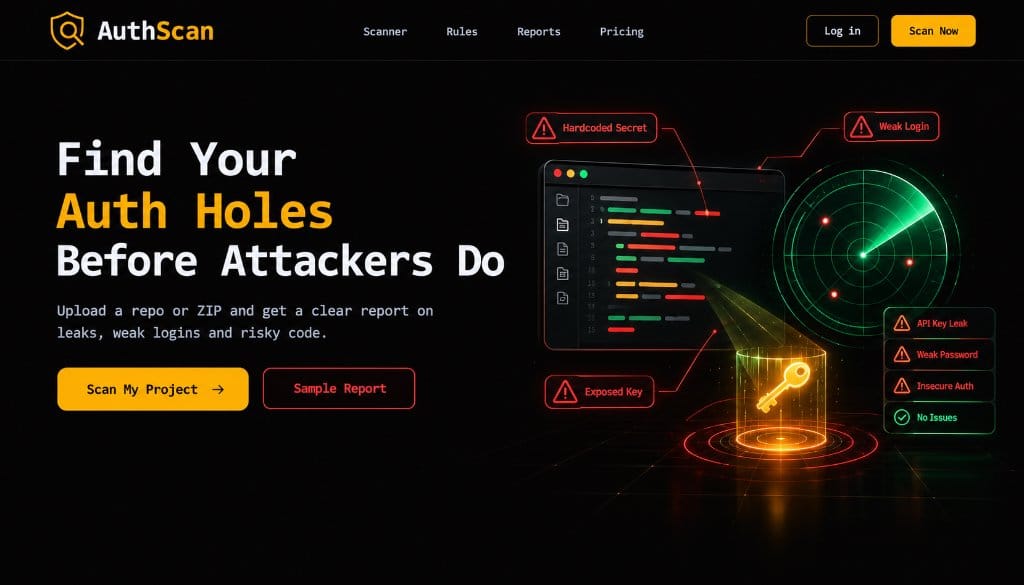
Find Your Auth Holes Before Attackers Do. Upload a repo or ZIP and get a clear report on leaks, weak logins, and risky code.
AuthScan
Co-Build (Opening Soon)
All ventures
Scanner Mode
Cloud Repo + Local CLI
Detection Engine
Deterministic Rule Packs
Threat Mapping
OWASP • CWE • MITRE
Product Capabilities & Architecture
10 Production Features

Exhaustive System Features & Workflow

Authentication Logic & Access Control Analysis

AST and pattern rules detecting broken password reset enumeration, session fixation, and weak Argon2id/bcrypt salts
Comprehensive JWT inspection checking for alg: none acceptance, short expiration times, and token storage in localStorage
Broken access control and IDOR pattern scanner identifying unauthenticated backend API endpoints and missing role checks
OAuth 2.0 and OIDC configuration auditor detecting open redirect URIs, missing state parameters, and PKCE omissions

Secrets Detection & Git History Scraper

Deep Git history commit scraper revealing secrets removed from head branches but still exposed in repository commits
Over 500 verified secret signatures spanning AWS, Google Cloud, Razorpay, Stripe, and private SSH certificates
Credential masking in all reports, ensuring discovered secrets are never logged or exposed in plaintext
Optional safe validation checks testing whether leaked key formats remain active to prioritize rotation urgency

Attack Path Modeling & Threat Scenarios

Attack chain synthesizer mapping multi-vulnerability exploit vectors into executive-level risk narratives
Direct cross-referencing with OWASP Top 10, OWASP API Security, CWE definitions, and MITRE ATT&CK techniques
Letter-grade security scores (A to F) broken down by authentication, credentials, data exposure, and dependencies
India-aware regulatory checks flagging unencrypted Aadhaar number storage and DLT SMS OTP pumping risks

CI/CD Automation & Remediation Pull Requests

Air-gapped local CLI mode (npx authscan .) analyzing code entirely offline with zero source code leaving the machine
GitHub Actions and GitLab CI quality gates automatically blocking merges when critical auth flaws are detected
One-click automated pull request generation applying framework-specific remediation code and cookie flags
Full SARIF import support for GitHub Code Scanning alerts and CycloneDX software bill of materials (SBOM) generation

All Individual Feature Specifications:

01Three Flexible Submission Modes: Scan via connected GitHub/GitLab repositories, drag-and-drop ZIP archives, or run the zero-leak local CLI binary (npx authscan .)
02Dedicated Authentication Logic Review: Identifies weak JWT signing (alg: none), missing OTP rate limits, session fixation, open OAuth redirects, and IDOR access control holes
03Deep Git History Secret Scanner: Uncovers committed API keys, cloud tokens, database URLs, and private certificates even if deleted from the latest commit
04Plain-Language Threat Scenarios: Translates abstract CWE numbers into actionable attack stories ('Anyone who can read this repo can forge admin tokens—here is how and how to fix it')
05Attack Chain Threat Modeling: Maps how combining a leaked credential, unthrottled reset flow, and missing CSRF header produces full account takeover
06India-Specific Compliance & Data Guardrails: Scans for unencrypted Aadhaar, PAN, UPI identifiers, and DLT SMS OTP pumping risks mapped to DPDP Act 2023 mandates
07Automated One-Click Fix PRs: Generates safe pull requests applying secure cookie attributes, .gitignore entries, and updated cryptographic hashing functions
08Multi-Format Export & Badges: Generates executive PDF summaries, technical SARIF reports for GitHub Code Scanning, CycloneDX SBOMs, and README security badges
09Factual AI Chatbot Explainer: Conversational assistant clarifying scan findings and providing framework-specific remediation guidance without touching raw code
10LoginKit Integration Verifier: Built-in validator verifying that applications using LoginKit implement token verification, callback routing, and sessions correctly
Visual Interface Showcase

Screenshots & Interaction Design

Screenshot Slots Ready

High-resolution interface viewports ready to link direct screenshots and walkthrough captures.

https://authscan.app
DESKTOP VIEW
AuthScan Primary Application View
Active Production View: AuthScan
FEATURE DETAILVIEWPORT 02
Interactive Workspace ViewSlot for modal, editor, or action flow preview.
MOBILE ADAPTIVEVIEWPORT 03
Mobile & Tablet ResponsiveSlot for touch-screen mobile viewport screenshot.
The Friction

Who experiences this problem?

Full-stack developers, engineering leads, security consultants, bug bounty hunters, agencies delivering client applications, and companies preparing for SOC 2 or investor diligence.

Current Workflow Breakdown:Generic static analysis tools burying developers in false positives, lack of focus on complex authentication bypass chains, and reluctance to upload proprietary source code to cloud servers without an offline CLI mode.
The Architecture

How our product addresses it

A specialized, defensive security scanning engine that inspects repositories, ZIP uploads, or local code via CLI. Employs deterministic static rules to detect authentication logic flaws, leaked cloud credentials across Git history, unencrypted PII, and vulnerable dependencies, generating executive letter grades (A–F) and copy-paste code fixes with zero black-box AI hallucinations.

Technical Stack & Foundations

Tree-sitter AST & Semgrep Static Rule Engine
Gitleaks Deep Git History Commit Crawler
OSV & NVD Dependency Vulnerability Graph
Air-Gapped Local CLI Scanning Mode (npx authscan)
SARIF & CycloneDX SBOM Export Pipelines
Isolated MicroVM Sandbox Analysis Containers
Attack Chain & Threat Scenario Synthesizer
Automated GitHub Pull Request Fix Generator
Milestones & Next Horizon

Current progress and roadmap

Stage: Building

Publishing the open-source CLI scanner binary (npx authscan .), packaging the first 100 Semgrep authentication rules, and integrating GitHub Actions CI/CD check suites.

Explore More

Other studio initiatives

LeadPilot
LeadPilot
You approve. It does the chasing.
ProductAI & Developer Tools
Building
LeadPilot logo

LeadPilot

An AI sales assistant that finds leads, writes your pitches, replies on WhatsApp and writes notes after every call.
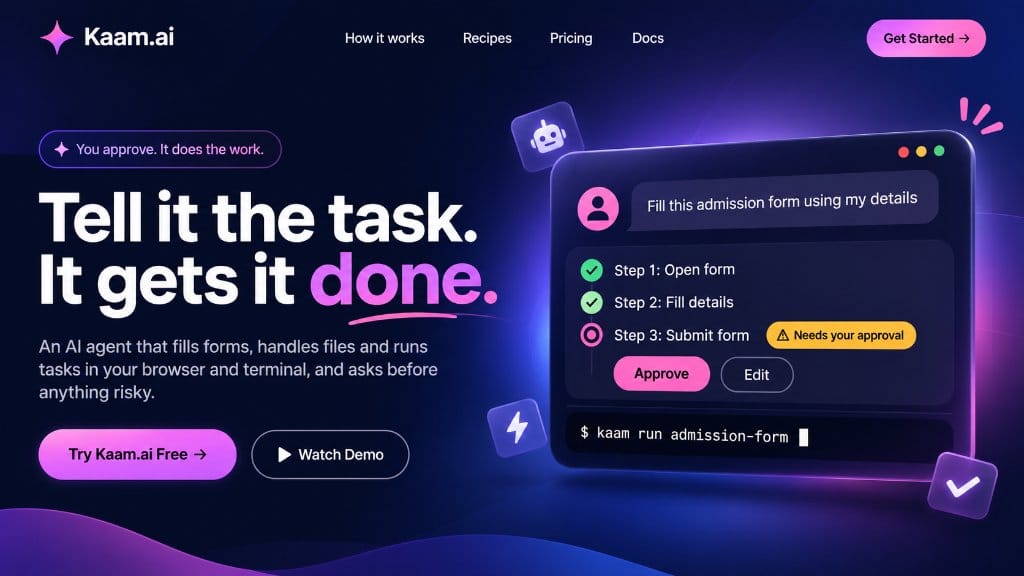
Multi-Source Lead Radar: Continuously scans Upwork, Fiverr, LinkedIn Jobs, RemoteOK, Reddit, X (Twitter), Google Maps, and public business directories for live hiring intent
AI 0-100 Lead Scoring: Rates every lead based on skill alignment, budget readiness, urgency, and reply probability so you only prioritize high-yield opportunities
Zero-Ban 'Draft & Approve' Guard: Generates tailored proposals and pitches for user 1-click review, preventing automated bot detection and protecting platform accounts from bans
+6 more technical capabilities
Studio-built
Kaam.ai
Kaam.ai
You approve. It does the work.
ProductAI & Developer Tools
Building
Kaam.ai logo

Kaam.ai

An AI agent that fills forms, handles files and runs tasks in your browser and terminal, and asks before anything risky.

Autonomous Form Filling: Navigates multi-page application forms, auto-mapping user profile data into input fields with pixel-level precision
Risk-Aware Approval Gates: Pauses before critical actions like 'Submit Form', 'Delete Files', or 'Execute Payment', requesting clear user confirmation
Kaam Terminal CLI: Trigger and run entire automated workflows directly from your terminal using commands like `kaam run admission-form`
+4 more technical capabilities
Studio-built